
Skip to content
Ingkle

Products

Operate NAZARE and NAVIS within each site’s permissions.

NAZARE separates data access by site and user. NAVIS connects the sources, tools and approvers required for each role. Explore separated operation and execution permissions across sites.

NAZARE + NAVIS

Match data and action permissions to each site and role

  1. 01NAZARE Separate operating spaces

    Separate data and settings by site or company

  2. 02NAZARE Set data permissions

    Assign equipment and menus to teams and users

  3. 03NAVIS Define AI access

    Connect permitted sources, tools and approvers

  4. 04NAVIS + NAZARE Review actions and operation

    Review who approved an action and what changed

NAZARE

Keep site data and permissions distinct.

NAZARE supports separate operating spaces for companies or sites and equipment and menu permissions for teams and users. Define how production data and site know-how are shared across multiple operations.

Explore the product capability
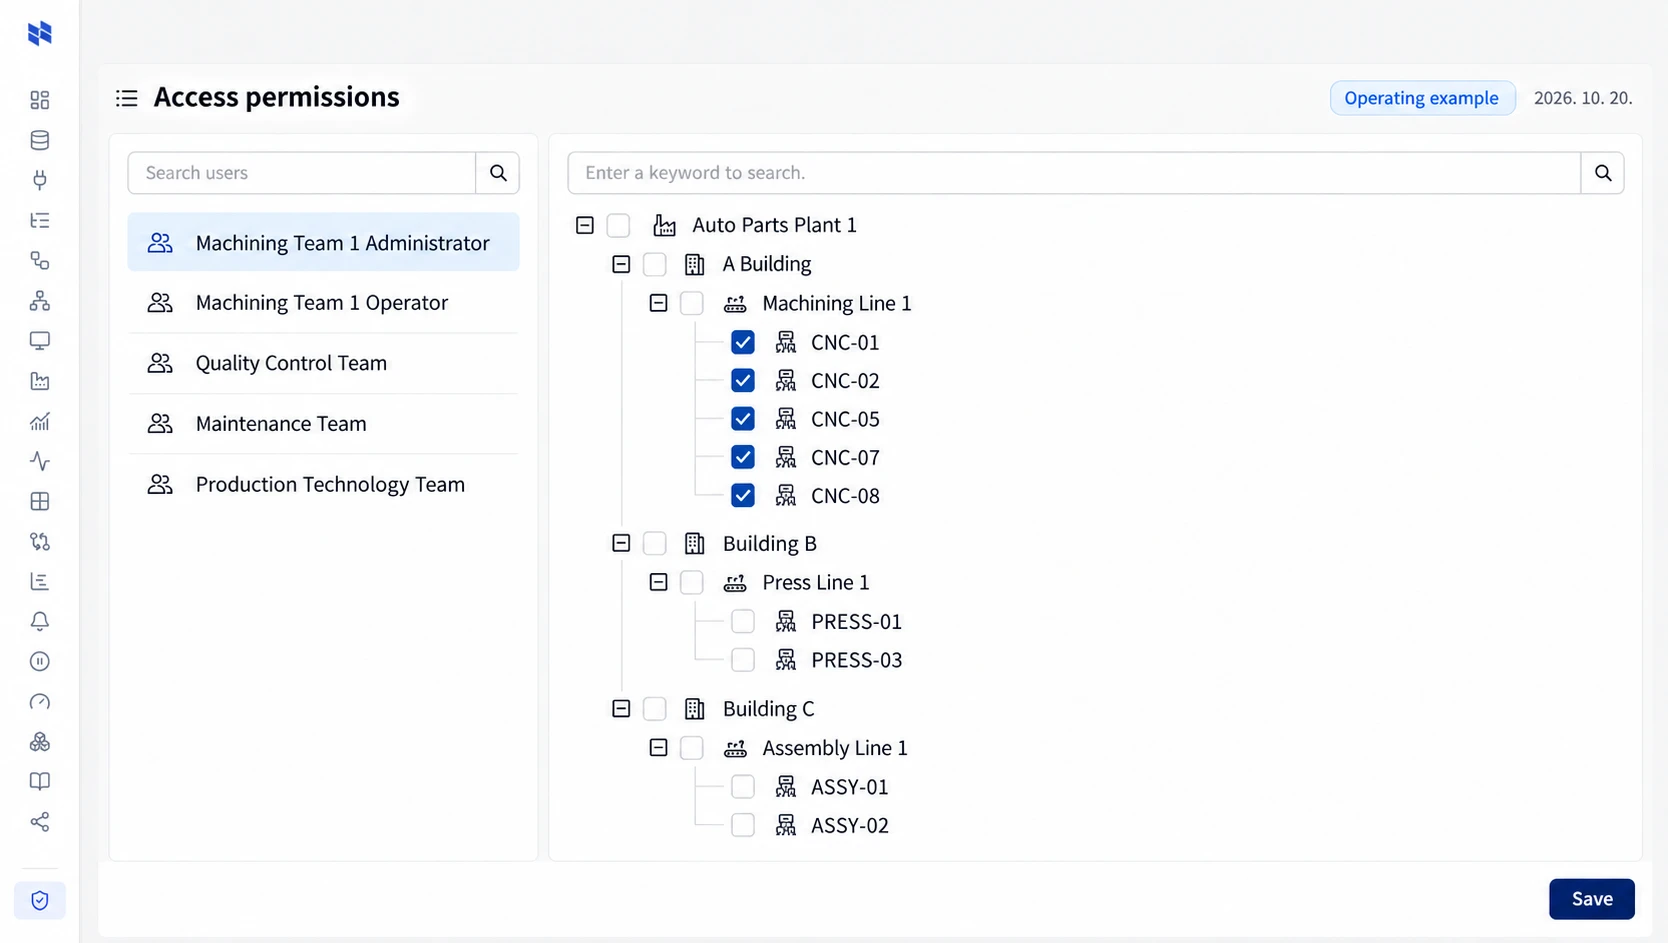
NAZAREEquipment access permissions
Equipment access permissions

NAVIS

Keep AI actions within assigned roles and approvals.

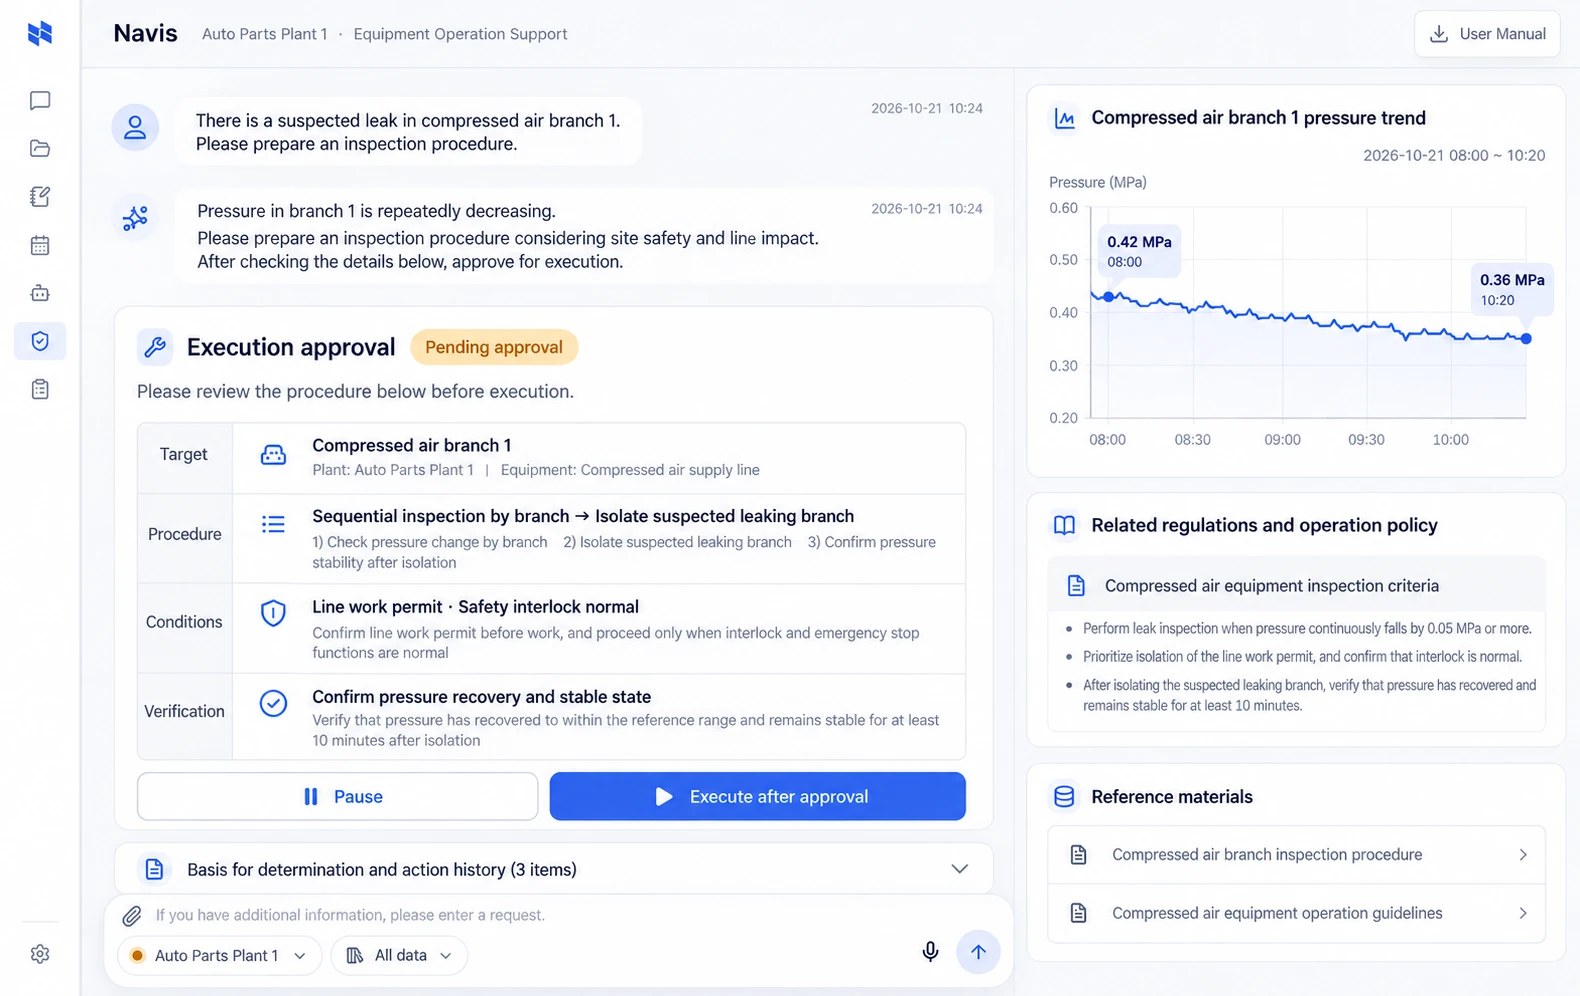
Connect the sources and tools needed for each role to NAVIS and designate who reviews execution requests. Approved equipment control passes through NAZARE, with results verified and retained as operating records.

Explore the product capability
NAVISApproval & execution
Approval & execution

Details

Scope and considerations

More factories, with clear data and action permissions

Define separate operating spaces and team and user access in NAZARE. Specify which equipment data, site knowledge, menus and analysis resources each group may use.

Configure NAVIS with the sources and tools needed for each role. Separate read access from action approval, and send equipment control requests to NAZARE after manager approval. As new sites are added, register their equipment, users and approvers under the same operating principles.

Independent tenant spaces

Shared hubs need separation as well as collection. NAZARE supports tenant-isolated data, settings, users and analytical resources, independent sandboxes, data marts and pipeline history.

Resource quotas and network policies limit cross-tenant impact. Define shared and private datasets at the start.

Encryption and resource allocation

Configurations support Parquet Modular Encryption with tenant-specific keys and encrypted transport such as TLS. Key creation, custody, revocation and query access must be managed together.

VM requests specify CPU, memory and disk for administrator approval and allocation, with Linux/Windows guests and create, change, return and status management. Virtualization infrastructure and physical procurement are scoped separately.

Hub acceptance criteria

  1. Verify cross-tenant data, configuration and user isolation.
  2. Test delegation and revoked access.
  3. Validate quotas during high analytical load.
  4. Review key recovery and backup procedures.
  5. Agree retention, export and offboarding rules.

Data trading, billing and integrated ROI services are separate service scopes.

Start together

Tell us what you want to improve first.

Tell us about your equipment, data and priorities to review a path from connection to operations.

Talk to Ingkle